Alert Advisory: Customer Advice Regarding the AnyDesk Incident

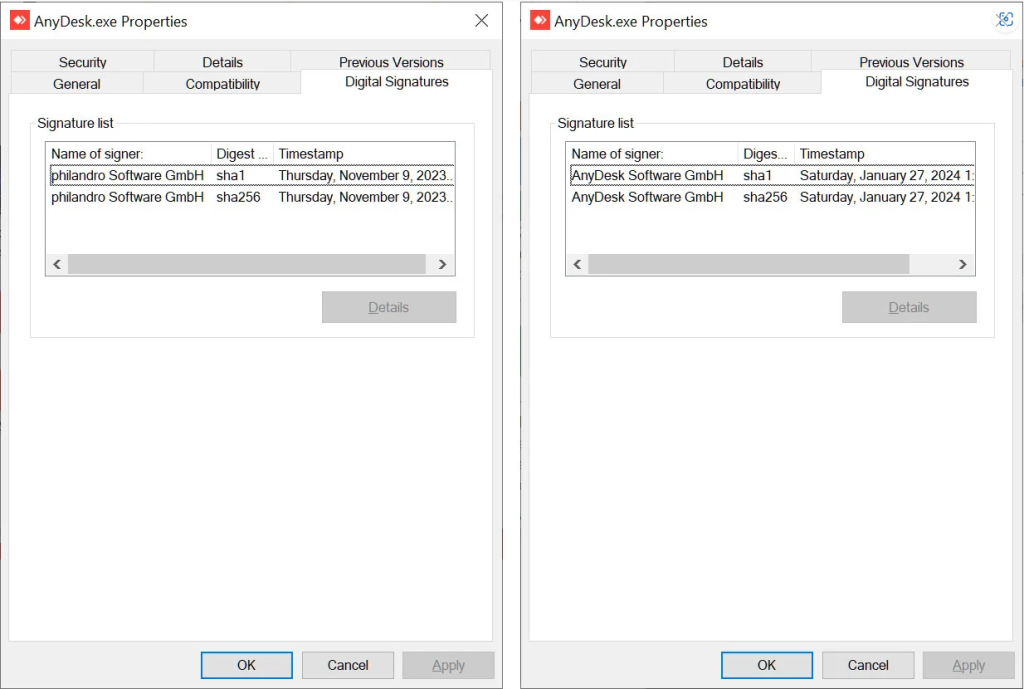
The following query can be used to locate executables in an environment that were signed with the previous, to-be-revoked certificate (including prior versions of the Anydesk client):
DeviceFileCertificateInfo
| where TimeGenerated >= ago(31d)
| where CertificateSerialNumber == “0dbf152deaf0b981a8a938d53f769db8”
and Signer == “philandro Software GmbH”
| project TimeGenerated, DeviceName, CertificateSerialNumber, Signed
It is strongly suggested that all users install the most recent version of the software (version 8.0.8 for Windows; other binaries continue to utilize the old certificate), as the old code signing certificate will be revoked soon. Anydesk has initiated a mandatory password reset for their customer portal, my.anydesk.com, and has advised users to update their passwords. Users are urged to also change any identical passwords used on other portals.
This week’s cybersecurity developments highlight the growing sophistication of modern threats and the need for a proactive and resilient security […]
Check Point revealed an arbitrary file read vulnerability impacting Check Point Security Gateways on May 28th, 2024. With a CVSS […]
PHP Critical Remote Code Execution PHP2Shell (CVE-2026-109618, CVE-2026-109619, CVSS 9.2) Overview Two critical RCE vulnerabilities in PHP (CVSS v4.0 9.2) […]